[ Gap 01 ]
Pre-execution policy verdicts
Every request gets a verdict before anything runs. ALLOW, BLOCK, MODIFY, or held for a named person — decided deterministically, not by a model. Nothing executes until the policy says so.
[ AI + MCP Gateway ]
Govern what your AI assets do, before they do it.
One gateway for model calls and tool calls. The rules, the scanning and the record are built in, so security is not a second vendor.
Routing, tool rules, scanning and the record ship together. One place routes each model call and decides each tool call.


Your SDK to your providers. Routing, fallback, caching and residency per key.
FallbackGive each agent its own key. Budget, rate limits, expiry and scope on each.
Decided before the call runs. By rules, not a model.
100 connectors, credentials sealed. A call not offered never runs.
Scans what goes in and out. In prompts, replies and tools.
One sealed record per request. No record, no run, by default.
Agents as governed tools. Versioned, on their own keys and run limits.
Attacks your agents and MCP servers. Findings you can recompute yourself.
Inside Verosek
Your SDK to your providers. Routing, fallback, caching and residency per key.
FallbackGive each agent its own key. Budget, rate limits, expiry and scope on each.
Decided before the call runs. By rules, not a model.
100 connectors, credentials sealed. A call not offered never runs.
Scans what goes in and out. In prompts, replies and tools.
One sealed record per request. No record, no run, by default.
Agents as governed tools. Versioned, on their own keys and run limits.
Attacks your agents and MCP servers. Findings you can recompute yourself.
Routing gets a call to a model. These five decide what happens next.
Routing, tool rules, scanning and the record ship together on one key. A security check is not a second vendor to buy, review, pay and log in to, and what it found lands in the same sealed record as the call.
Keep your SDK.
Keep your models.
Keep your code.
import openaiclient = openai.OpenAI(api_key="vsk_...",base_url="http://your-gateway/v1",)
Keep your OpenAI, Anthropic or Gemini SDK and change two values.
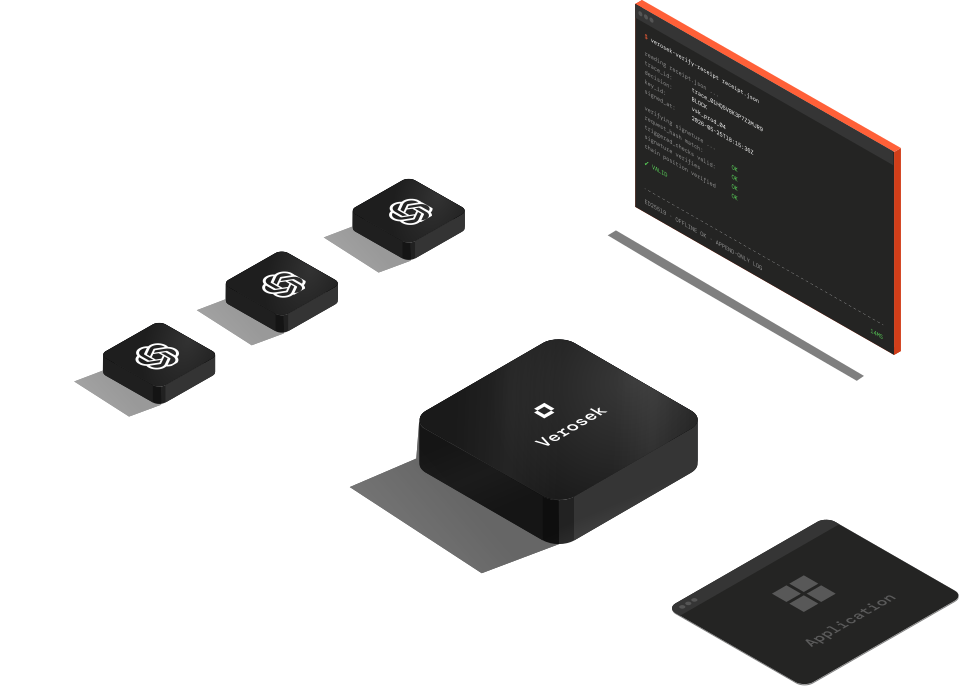
On a self-hosted deployment, an auditor verifies each receipt with no network call back to Verosek.
Assay, an open MCP security benchmark we maintain, was presented at Black Hat India Arsenal. Our red-team framework holds 205 attack techniques, 68 for MCP, with findings anyone can recompute. Attacks become findings, and findings become rules on the key.
And we are just getting started...
Indirect injection through tool returns is the gap in agent safety. Verosek scans for it. The cumulative session-level monitoring also catches the slow distributed version. From a research standpoint, that's the right place to put the work
Sumeet Motwani
Oxford ML PhD, ex-BAIR, alignment researcher
When you're running agents in production, key-level access isn't enough. I want one agent to read a table but not modify it, or hit one endpoint but not the next. Verosek draws that line per tool and per argument.
Sarvagya Kulshrestha
Founder, Backdoor (Ex-Antler, Seekho, OTPless)
Keep building, you do great stuff
Dane Knecht
CTO, Cloudflare
Fifteen years in infra, same lesson every time: fail-open is a fiction people end up regretting. Verosek's fail-closed default with an SDK circuit breaker is the right posture for production. If the policy layer is down, the call doesn't land. Full stop.
Rushabh Shah
15+ yrs infra & security leadership (EY Parthenon, Lyft, Dialpad, Cisco, Vox)
Building across multiple AI surfaces, you end up writing wrapper code per provider. Verosek lets the same client hit OpenAI, Anthropic, or Gemini without rewriting anything. One integration point, one audit trail, regardless of which model is running underneath.
Viren Inaniyan
Co-Founder/CEO, TruCommerce (IIT Bombay)
Coming from fintech ops, the compliance posture is what stands out. Mapped reports for NIST AI RMF and EU AI Act, signed traces an outside auditor can verify offline, deployment that keeps data inside your VPC. That's the unglamorous list that decides whether AI agents clear procurement.
Tanish Shah
EIR @ Trueway, ex-PhonePe, ex-Roland Berger (IIM Calcutta, BITS)
The interesting design choice: the policy engine is deterministic and version-controlled. A table of checks you can read, diff, and reason about. Not an LLM judging each call. For something in the request path, that's the only approach that holds up under review.
Pratham Grover
ML, Microsoft Core AI (Ex- Siemens, Samsung)
And we are just getting started...
Indirect injection through tool returns is the gap in agent safety. Verosek scans for it. The cumulative session-level monitoring also catches the slow distributed version. From a research standpoint, that's the right place to put the work
Sumeet Motwani
Oxford ML PhD, ex-BAIR, alignment researcher
When you're running agents in production, key-level access isn't enough. I want one agent to read a table but not modify it, or hit one endpoint but not the next. Verosek draws that line per tool and per argument.
Sarvagya Kulshrestha
Founder, Backdoor (Ex-Antler, Seekho, OTPless)
Keep building, you do great stuff
Dane Knecht
CTO, Cloudflare
Fifteen years in infra, same lesson every time: fail-open is a fiction people end up regretting. Verosek's fail-closed default with an SDK circuit breaker is the right posture for production. If the policy layer is down, the call doesn't land. Full stop.
Rushabh Shah
15+ yrs infra & security leadership (EY Parthenon, Lyft, Dialpad, Cisco, Vox)
Building across multiple AI surfaces, you end up writing wrapper code per provider. Verosek lets the same client hit OpenAI, Anthropic, or Gemini without rewriting anything. One integration point, one audit trail, regardless of which model is running underneath.
Viren Inaniyan
Co-Founder/CEO, TruCommerce (IIT Bombay)
Coming from fintech ops, the compliance posture is what stands out. Mapped reports for NIST AI RMF and EU AI Act, signed traces an outside auditor can verify offline, deployment that keeps data inside your VPC. That's the unglamorous list that decides whether AI agents clear procurement.
Tanish Shah
EIR @ Trueway, ex-PhonePe, ex-Roland Berger (IIM Calcutta, BITS)
The interesting design choice: the policy engine is deterministic and version-controlled. A table of checks you can read, diff, and reason about. Not an LLM judging each call. For something in the request path, that's the only approach that holds up under review.
Pratham Grover
ML, Microsoft Core AI (Ex- Siemens, Samsung)
One price per request: routing, rules, Shield and a sealed record are all in it. You pay your model providers directly, with no markup from us. Enterprise can run wholly in your environment, with your own signing key.
Overage: $0.50 / 1k requests. Shield and the sealed record come with every request.
Verosek is an AI + MCP Gateway for AI agent security. It routes model calls and, for the tools it runs, reads what each call does, down to the SQL statement, then decides it against the agent key's rules before it runs. Scanning and a sealed record of each request ship in the same product.
Platform and infrastructure teams putting AI agents into production on real data, and the security reviewers who sign off on them.
Verosek decides SQL from the statement itself, and seals a record of each request, on one key with routing, budgets and scanning. Many gateways now route model calls and cover MCP tools, so choose by how far a rule must read a tool's arguments, what should happen when a check fails, and who has to check the record later. Our comparison page sets six tools side by side and lists its sources at the foot.
Verosek starts with a call. We set it up with you, and you get a gateway URL and a first key. On the Enterprise plan we deploy it with you in your environment. Then two values change in your code: the SDK's base URL and its API key. See how it works.
Team is $999 a month, billed yearly, with 25 virtual keys, 5 MCP connections and 500k requests a month. Enterprise has custom terms and limits. Both plans start with a call. See pricing.
We set it up with you on a call, and you get a gateway URL and a first key. On the Enterprise plan we deploy it with you in your environment: your own VPC or on-prem. The gateway runs where it can reach your MCP servers and databases.
Yes. The self-hosted and on-prem deployments run fully offline — no outbound calls to Verosek are required for the gateway, Shield, or audit signing.
Under 30ms P99 for routing and deterministic checks; offline ML checks add a few milliseconds depending on the profile you enable.
All credentials are encrypted at rest with AES-256-GCM.
On a self-hosted deployment, on the Enterprise plan, you do.
On a self-hosted deployment, yes. Every receipt is HMAC-SHA256 signed and chained; an auditor you give the verification key can verify the full chain offline with a single CLI command, no call back to Verosek.